
Martyn’s Law Compliance: Preparing for the Terrorism (Protection of Premises) Act 2025
Last reviewed: October 2026. This page summarises official guidance and is not legal advice.

What is Martyn’s Law?
Martyn’s Law is the Terrorism (Protection of Premises) Act 2025. It requires those responsible for certain publicly accessible premises and events to be prepared to respond to a terrorist attack, and asks larger premises and events to also take steps to reduce their vulnerability.
The Act is named after Martyn Hett, one of the 22 people killed in the Manchester Arena attack in May 2017, and was championed by his mother, Figen Murray OBE, whose campaign ran for the best part of a decade.
The Act received Royal Assent on 3 April 2025 but is not yet in force. The Security Industry Authority (SIA) will regulate it. The government has committed to an implementation period of at least 24 months, and commencement is expected in spring 2027.
Does Martyn’s Law apply to your venue or event?
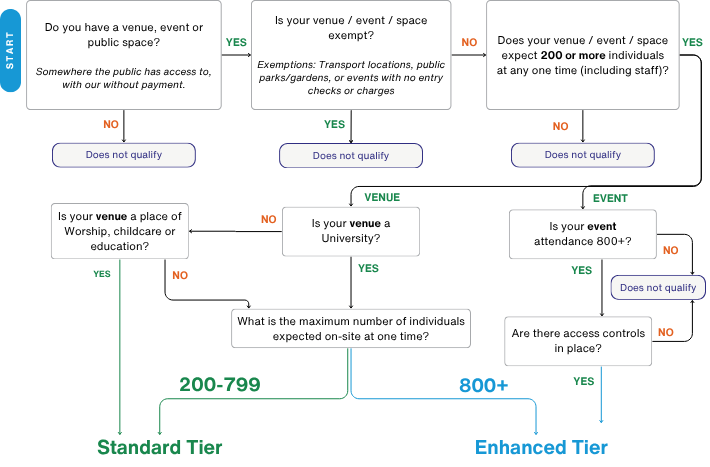
It depends on how many people you can reasonably expect to be present at the same time, staff included, and on what the premises are used for. Premises used for listed purposes fall into one of two tiers: Standard or Enhanced.
A few things catch people out:
- Your tier depends on the number you can reasonably expect, not your licensed capacity. Even a figure reached only occasionally counts.
- A venue that is usually standard tier can host a one-off qualifying event that falls under the enhanced tier.
- Places of worship stay in the standard tier at any size.
The official scope factsheets set out the listed uses and exemptions in full.
Assess Your Current Incident Response Processes
If you’re still working out where to start, begin with your current response process. Our Incident Response Assessment is a dynamic, insight-driven tool designed to help safety and security teams assess, understand and improve their incident response capabilities.
What does Martyn’s Law Compliance Require?
The Act sets out four things, scaled by tier. Every duty applies “so far as is reasonably practicable”, so the expectation is proportionate.
Standard tier and above
- Notify the SIA that your premises or event is in scope.
- Have public protection procedures your staff can follow in an attack. These cover four areas: evacuation, invacuation (moving people to a safe place inside), lockdown, and communicating with people on site.
Enhanced tier and qualifying events, in addition
- Put public protection measures in place to reduce vulnerability, such as how people move into and around the site, how the site is monitored and how sensitive information is protected.
- Document your procedures and measures and appoint accountable leadership. That means a written record shared with the SIA and, where the responsible person is an organisation, a designated senior individual.
Penalties. Standard tier penalties are capped at £10,000, plus up to £500 a day for continued non-compliance. Enhanced tier penalties go up to £18 million or 5% of worldwide revenue, plus up to £50,000 a day. The SIA has said it will take a supportive, proportionate approach first.
Compliance vs Readiness
We think Martyn’s Law is a good thing. It gives venues and event organisers clarity on what the best operators already do: treating safety and security as part of how the place runs every day, ingrained within the culture of the organisation.
But a compliant plan and a ready operation aren’t necessarily the same thing. The Act asks you to have procedures. Readiness is whether those procedures hold up at 21:40 on a matchday. When a steward has seconds to act, the control room is taking radio traffic from three directions, and a contractor team hasn’t heard about last week’s change.
That gap is closed by people more than paperwork. It needs procedures short enough to use under pressure. Staff need to understand why a step matters, so they can adapt when the day doesn’t match the plan. Contractors should be briefed and reporting like everyone else. Information has to reach the control room while it can still change the outcome. And decisions, and the reasons for them, should be recorded at the time, not pieced together afterwards.
Technology has a part to play. One operational picture and a time-stamped audit trail make the last two far easier. But it isn’t the answer on its own. If reporting is patchy, or teams work around the system, digitising a muddled process just gives you a faster muddle.
There’s also time. With commencement expected in spring 2027, the implementation period is a chance to get this right deliberately, rather than buying something in a hurry.
Frequently Asked Questions
It is expected in spring 2027. The exact date has not been set and will be confirmed through Parliament. Until then, the duties are not enforceable and you don’t need to notify the SIA.
The Security Industry Authority (SIA). It can carry out inspections, issue compliance notices and impose penalties. It has said it will start with support and guidance before formal enforcement.
No. The Act requires procedures, and for the enhanced tier, measures and documentation. It does not require any particular technology. Systems can make information flow and record-keeping easier, but they are a choice, not a legal requirement.
Martyn’s Law asks you to have procedures, and to be able to show they work. The Halo System lets you run your pre-event checks from templates; link response checklists to the incidents they relate to in real time; download time-stamped, user-stamped reports, and more.
Learn more about The Halo System →
Most will be, because they can reasonably expect 800 or more people at the same time. Tier depends on the listed uses and the expected number of people, so check the official scope factsheets rather than assuming.
The “responsible person”: whoever controls the premises, or who is responsible for the event. Where that is an organisation in the enhanced tier, it must also designate a senior individual.
Assess Your Current Incident Response Processes
If you’re still working out where to start, begin with your current response process. Our Incident Response Assessment is a dynamic, insight-driven tool designed to help safety and security teams assess, understand and improve their incident response capabilities.
Official Sources
For the definitive position, go to the official sources:
- Terrorism (Protection of Premises) Act 2025 factsheets (Home Office, GOV.UK)
- Martyn's Law guidance and updates (Security Industry Authority)
- Martyn's Law hub (ProtectUK)
Disclaimer: This page summarises publicly available guidance as at the date shown. It is not legal advice. Check the official sources, or take legal advice, for your specific premises or event.